A policy can govern a request only when that request reaches the control. For automated cloud changes, trace the actual path before judging the guardrail.
A proxy checks cloud API requests
Cloudflare’s October 19 announcement introduces Cloud Workload Security in beta. A Zero Trust subscription is required, and the Free plan is sufficient for access.
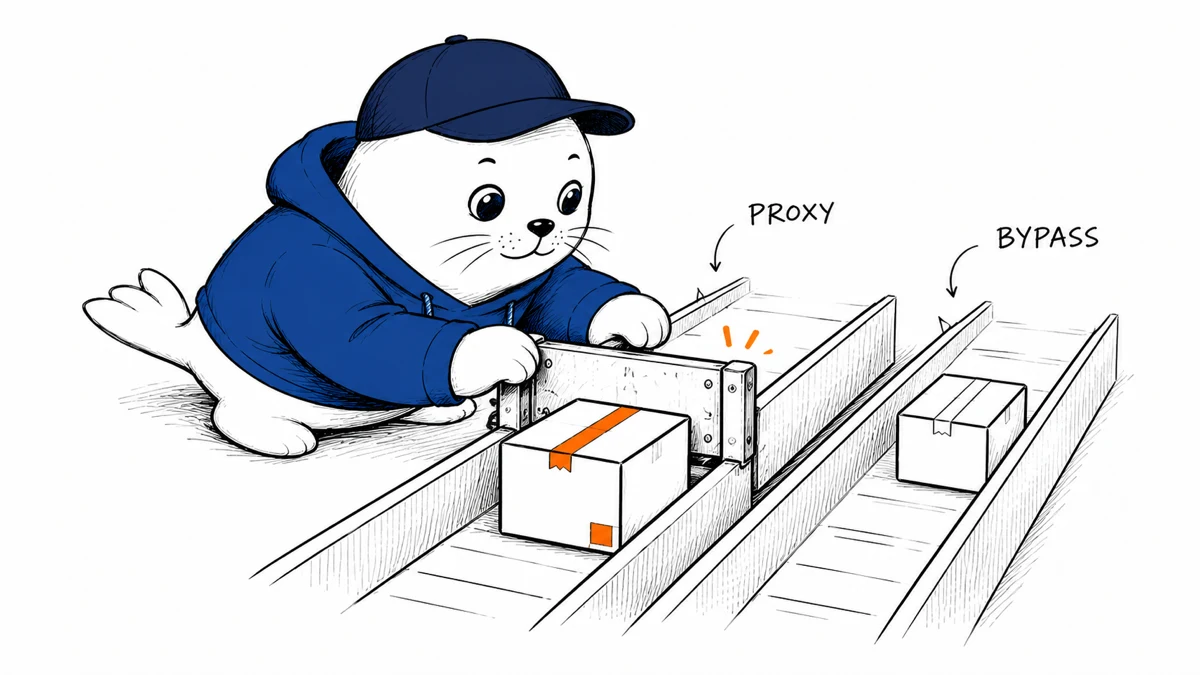
The documentation describes a proxy running in your environment. It evaluates routed requests before forwarding them to a cloud-provider API. This is a cloud API control that can apply to automated workloads; it is not limited to AI agents.
The policy and its deployment both matter
Request filters select the traffic to be evaluated, and Rego expressions make policy decisions. Policy sets must be attached to the relevant deployment. Enforcement must be configured to block requests.
Review the default action for unmatched requests and the on-error action for policy failures. Domain access rules address destinations separately. A policy expression by itself does not establish what happens to every request.
Test one allowed change and one denied change
Cloudflare documents an example of how to prevent a public R2 bucket. In an isolated test account, a reviewer could use a similar bounded rule to check an allowed private operation and a deliberately denied public configuration.
- Confirm that the workload sends the test requests through the proxy.
- Verify the selected policy set, workload filters, and enforcement mode.
- Check the upstream resource state after the allowed request.
- Check that the denied operation did not create the unwanted state.
- Exercise an unmatched request and a controlled policy error.
- Inspect whether another network path can bypass the proxy.
Report coverage with the result
A blocked request demonstrates behavior on that tested path. It does not establish protection for traffic that never passed through the proxy. Record the workload, destination, policy version, and observed result together.
I would include bypass paths in the review rather than count only the successful deny test. We have not run an attack simulation or independently evaluated the beta’s effectiveness. The useful next step is a controlled deployment test with a clear rollback.
Our Replit deployment-boundary guide separates hosting location from operational responsibility. The AI Search update covers a separate Cloudflare product.
Read the sources and plan your next step
Can you demonstrate which cloud API requests pass through the control?
Checked October 19, 2026. This is source-based reporting and analysis; proposed checks are not hands-on test results.