An agent can keep the same task while its permissions need to change. Test whether the enforcing system can narrow that access while the agent is still working.
Perception expands beyond model selection
Microsoft’s October 19 announcement extends Project Perception to securing agents operating inside organizations. It describes Guardian Agents and task-scoped Dynamic Permissions.
Perception and Microsoft Agent 365 share a registry and security context. Microsoft says this helps teams identify agents and respond as their risk changes.
The earlier article focused on routing security work between models. The expanded announcement adds another decision: what authority an agent receives while doing that work.
Give the agent an accountable identity
Microsoft describes separate agent identities and permissions tailored to an approved task. Its principle is to keep enforcement outside the model being controlled.
A capable model can propose an action. A separate system must decide whether the agent has authority to take it. Keep the model choice and the permission decision separately observable.
I would start by assigning each granted operation an owner and a reason. A list of discovered agents is useful only when someone can act on a suspicious or obsolete entry.
Revoke a permission during an authorized trial
Use harmless documents in a controlled environment. Define the expected read and write operations before starting the task.
- Record the agent identity and accountable owner.
- Grant only the resources needed for the trial.
- Remove write authority while the task is active.
- Confirm that the enforcing system denies a new write request.
- Check whether the agent stops, continues safe reads, or asks for review.
- Save the denial and the resulting task state.
This proposed trial checks one permission boundary. It does not establish protection against every prompt injection or compromised runtime.
Keep model routing tied to evidence
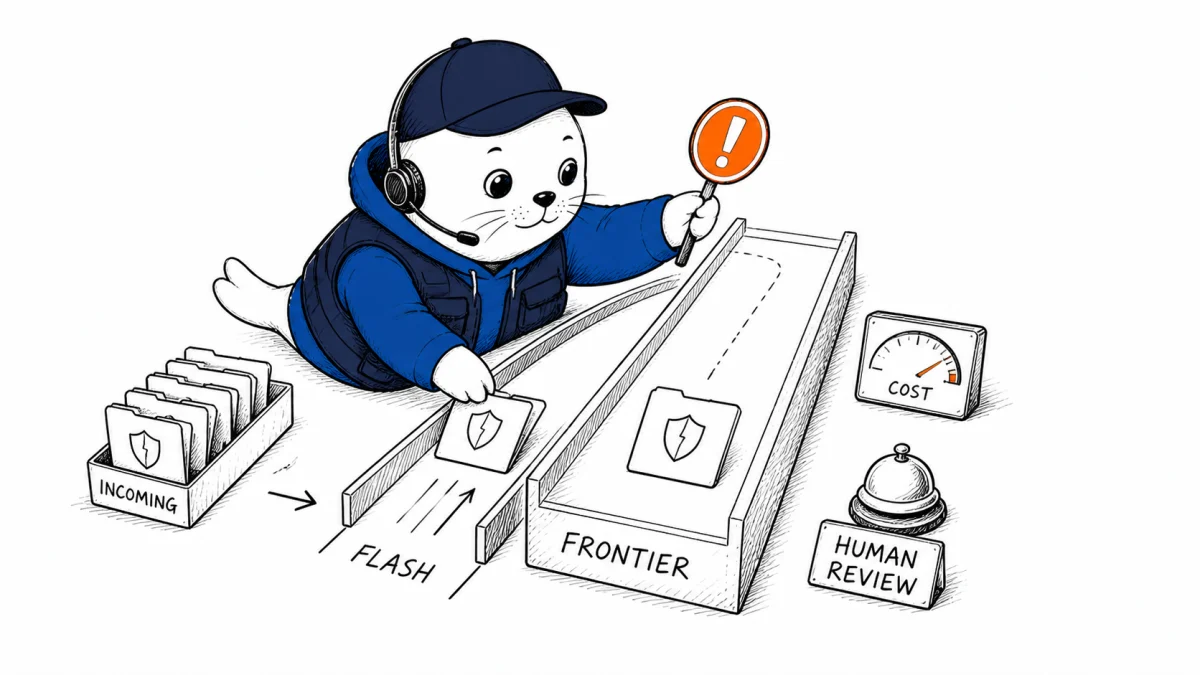
For security analysis, a smaller model may handle familiar cases while harder cases move to another model or a person. Evaluate that routing with the included errors and review work.
Count cases escalated after the first answer, and check the evidence supporting a remediation. A model score alone cannot validate permissions, approval rules, or production recovery.
Keep availability separate from the architectural proposal. The October announcement does not establish general availability of every described control. Confirm entitlement and supported integrations before planning deployment.
The Inference Hooks guide covers a policy endpoint outside the model. Our MCP authorization article examines another task-scoped access mechanism.
Read the sources and choose your next check
How would your team prove that a permission change took effect during a running task?
Checked October 21, 2026. This article is based on source review and analysis. Suggested tests have not been performed by MustHave.ai.