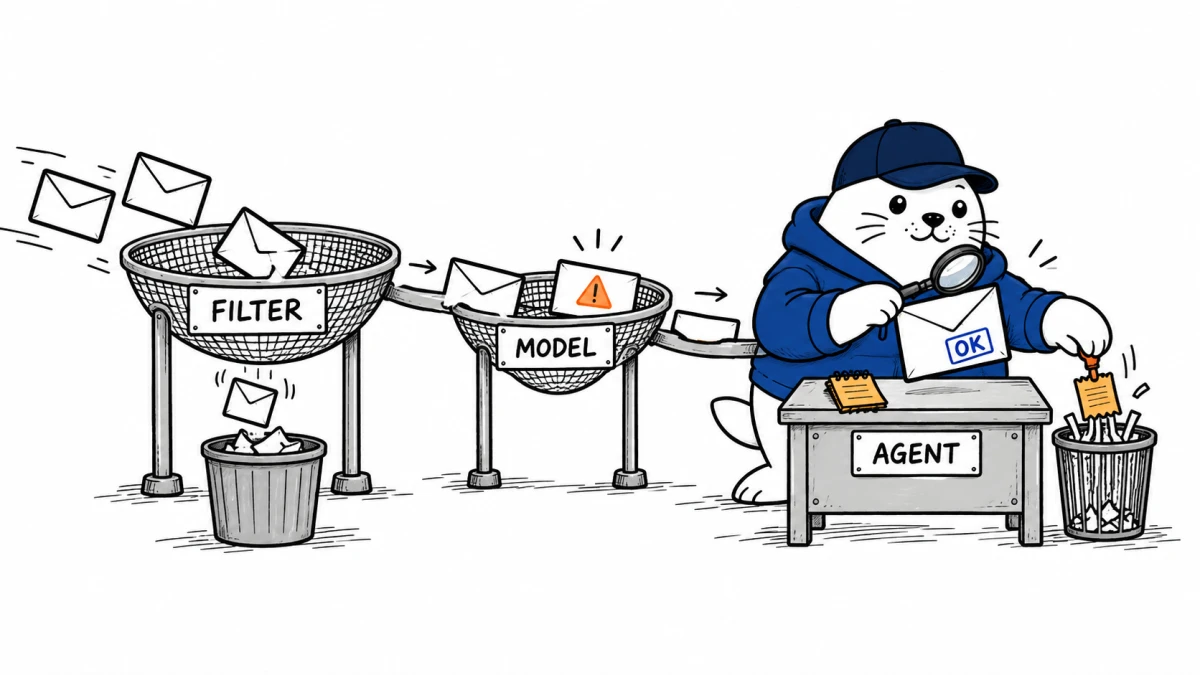
Abnormal AI says it does not send every email to a large agent. Its production design narrows the stream through heuristics and machine-learning models before code-executing agents examine tens of thousands of the hardest cases per day.
The architecture appears in an AWS customer case study published September 14, 2026. AWS says Abnormal AI protects more than 25 percent of the Fortune 500 and processes billions of messages. Those reach and scale figures are company-reported, not independently audited in the post.
The key design choice is progressive filtering
| Tier | Reported daily volume | Job | Why it belongs there |
|---|---|---|---|
| Heuristics and lightweight classifiers | Billions | Resolve obvious cases cheaply | Most messages do not need deep analysis |
| Deep learning and ML | Millions | Analyze uncertain behavioral signals | More context at a manageable volume |
| Inline agents with Code Interpreter | Tens of thousands | Investigate the hardest cases | Dynamic analysis is reserved for difficult decisions |
This table corrects a tempting but inaccurate reading of the case study: billions of messages enter the system, but only a much smaller final slice reaches inline agents. The expensive and risky capability sits behind two confidence gates.
Why an email-security agent needs a compute scratch pad
Language reasoning alone is weak at counting, aggregation, data transformation and reproducible verification. Abnormal’s agents use Code Interpreter to write scripts, analyze threat-intelligence features and test how evidence fits the behavioral model. AWS describes the sandbox as a fully managed serverless runtime rather than an agent framework that dictates the workflow.
The sandbox boundaries are part of the decision
- Ephemeral MicroVM sessions default to 15 minutes and can be configured up to eight hours.
- Sessions are isolated at the host operating-system level according to AWS.
- Networking can use a sandbox VPC mode or public internet access.
- Files up to 100 MB can move through the API, with S3 for larger data.
- CloudWatch and CloudTrail provide operational logs.
Ephemeral does not mean harmless. A long session, internet access and uploaded attachments can enlarge the blast radius. Teams need explicit limits for network destinations, file retention, secrets, execution time and output destinations.
A production control map for code-executing security agents
| Failure | Preventive control | Evidence to retain |
|---|---|---|
| Unsafe attachment or script | Content limits, isolated runtime and blocked persistence | Input hash, generated code and exit result |
| Unnecessary network access | Default-deny egress and allowlisted services | Connection log and policy decision |
| Agent overconfidence | Confidence gate and separate verification path | Signals, rationale and final disposition |
| Bad feedback entering Tier 1 | Offline evaluation before heuristic promotion | Regression set and reviewer approval |
The batch agent creates a second risk surface
Abnormal also describes an analyst agent that studies misclassifications and drafts candidate heuristics for earlier tiers. AWS says it runs about 100 batch jobs per week, with some sessions lasting more than 30 minutes and broader operations extending across a day. A draft rule that later filters billions of messages deserves stricter promotion controls than a one-off investigation.
The safest pattern is draft, replay, compare, approve and canary. Evaluate a candidate heuristic on recent false positives, known attacks and distribution shifts before it reaches the first tier.
What the case study does not prove
The AWS post does not provide an independent detection benchmark, false-positive rate, breach-rate comparison or external security audit of the agent path. It is valuable architecture evidence, not a product-effectiveness ranking. Buyers should ask for outcome metrics tied to their own mail population.
Our agent sandbox control guide covers code and computer-use boundaries. The multi-turn agent evaluation guide shows how to separate task completion from safe execution.
The practical verdict
Abnormal AI’s most transferable idea is not code execution by itself. It is reserving code-executing agents for a narrow residue after cheaper deterministic and statistical systems do the bulk of the work. In security, that routing decision can reduce cost, latency and attack surface at the same time.
Primary source
Checked September 14, 2026. Architecture, deployment and scale figures are AWS and Abnormal AI reported. MustHave.ai has not independently audited the system.