A sign-in you don’t recognize is easier to investigate if you can see when it happened and which device was used. ChatGPT now provides account holders with a security history view. It is useful evidence, but it is not a substitute for checking active sessions and securing the account.
Where to find ChatGPT security history
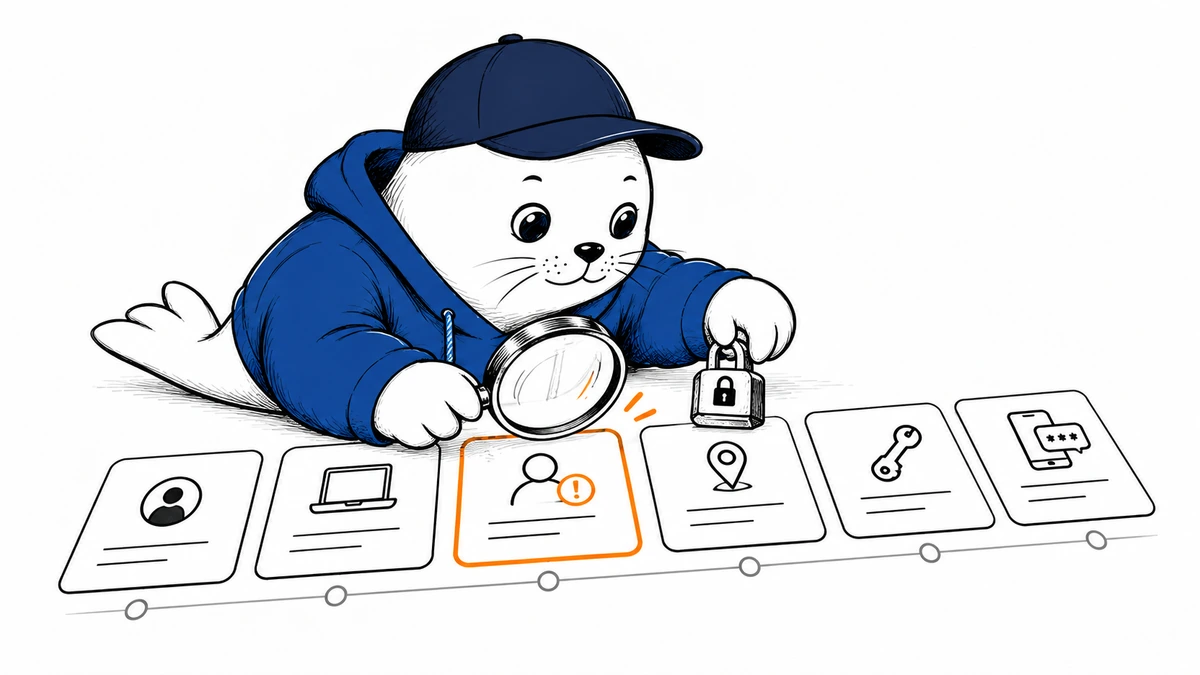
OpenAI added security history on September 25, 2026. On the ChatGPT website, open Settings → Security and login → Security history. The view records recent sign-ins, sign-outs, and changes to passwords, multifactor authentication, passkeys, and other security settings. Each event may include a time, location, and device. OpenAI warns that some details can be approximate or unavailable.
This view is an account-activity log, not a promise that every action inside a conversation will appear there. It is also not the same as the Active Sessions view. Security history tells you what changed; Active Sessions helps you see which sessions are currently signed in and manage them.
A five-minute check that can save a longer recovery
Start with the latest events and compare them with your devices and travel. A location mismatch is worth checking, but it is not proof of a takeover: location can be approximate. An unauthorized passkey or MFA change is a more direct signal. Record the event type, time, and device before changing settings so you retain useful details if you need support.
If an event looks unfamiliar, OpenAI’s account-security instructions say to change an exposed password, log out of all sessions, review security history, and contact support. If you use the API, check usage and revoke potentially exposed keys as well. OpenAI says logging out of other ChatGPT sessions can take up to 30 minutes. Enabling MFA by itself does not end sessions that are already active.
That order matters. Someone who has an existing session may remain signed in while you add a second factor. The practical sequence is to preserve evidence, change a compromised credential, end active sessions, and then strengthen sign-in protection. For teams, keep the support and API-key checks alongside—not buried inside—a consumer ChatGPT checklist.
What this changes for people using AI agents
More ChatGPT workflows now involve connected services and delegated actions. Our guide to Voice and connected apps explains how account access can carry through to other tools. Security history does not replace those tools’ own audit logs; it gives you one more place to check the OpenAI account at the center of the workflow.
It also differs from the re-authentication step GitHub recently added for some sensitive operations. That proof-of-presence change asks a person to confirm a high-impact action before it proceeds. ChatGPT security history is retrospective: it helps you inspect account events after they occur. Both ideas are useful, but they solve different parts of the trust problem.
The bottom line
Check security history now, while your own recent activity is still easy to recognize. Then look at active sessions. If you see a suspicious change, treat the history as evidence for an account-security response, not as an alert system that has already contained the incident. OpenAI has published the feature and the response steps; it has not promised perfect location accuracy or complete coverage of every account action.